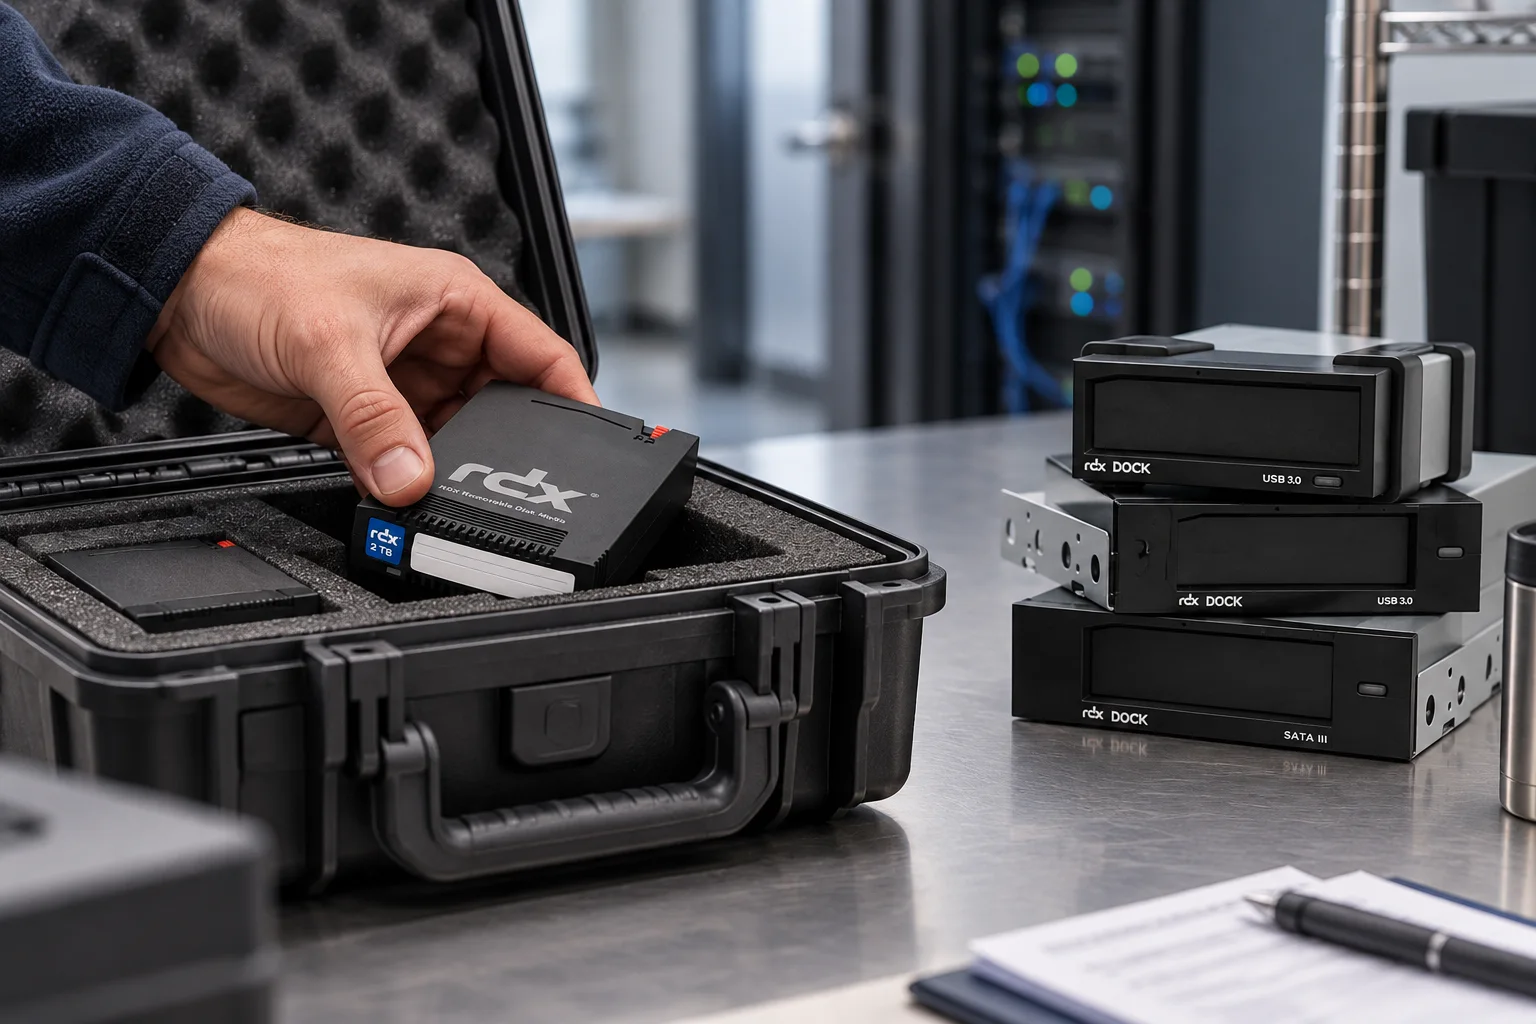
An off-site backup is not created when a drive leaves the office. It becomes useful when the organisation can prove which copy has left, who accepted it, where it is held, how it will be retrieved and what is required to restore from it. Without that chain, a physical move may add distance but not resilience.
This does not need an elaborate enterprise workflow. A small organisation can operate a strong off-site process if ownership, handover and recovery evidence are clear enough for someone other than the regular administrator to follow.
Define the role of the off-site copy
Start with the incident, rather than the storage location. Is the separated copy intended to protect against a building outage, a ransomware investigation, a hardware loss or a delayed discovery of data damage? How quickly might the team need the media, and who can access the secondary location outside normal working hours?
Those questions establish the purpose of the copy. A media store that is geographically separate but impossible to access within the required recovery window may still be valuable for retention, but it cannot be described as the immediate recovery path. Equally, a nearby copy may help ordinary restores without being sufficiently separated for a wider site incident. The design can use more than one recovery tier, provided each role is explicit.
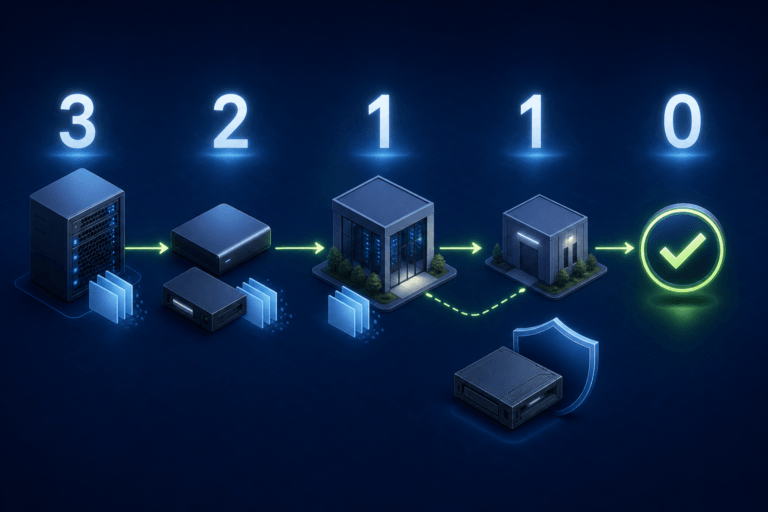
The 3-2-1-1-0 principle includes an off-site copy as part of a broader resilience approach. It is not a shortcut around restore testing, availability of the backup software or the operational controls that make the copy retrievable.
Choose a secondary location with recovery in mind
The right location is not simply the furthest address. Assess whether it is subject to the same practical risks as the primary site, whether authorised people can access it when required, and whether the organisation can retrieve media without relying on one unavailable individual. Consider the normal route as well as an exception: a transport disruption, a facility closure or a change of custodian.
Contractual, insurance, privacy and retention constraints vary by organisation and jurisdiction. This article does not state where any particular data must be kept. Those requirements should be confirmed by the organisation with the appropriate advisers before a third party or external location is used.
Turn people into named responsibilities
Most off-site failures are ordinary operational failures: a person assumes someone else took the drive, an overdue item is noticed too late or a stand-in does not know who can release it. Assign four functions, even if a small team gives more than one to the same person:
- confirm that the selected backup job has completed and is suitable for handover;
- prepare and release the medium;
- receive or safeguard it at the destination;
- monitor exceptions, returns and approved reuse.
For each function, identify a cover person and an escalation route. The process should explain what happens when the scheduled carrier is absent, the destination cannot acknowledge receipt or a backup result needs investigation. A schedule is useful, but a safe exception process matters more than keeping a schedule at any cost.
Use identifiers that help recovery without revealing data
Give every removable medium a permanent, non-sensitive identifier. It might be a rotation number or controlled asset reference. The identifier links the physical item to the register; it should not reveal customer names, folder names, account details or recovery credentials.
Keep the operational record separate from access information. The register records the information a recovery team needs to locate and govern the item. Instructions, credentials and encryption material require the organisation’s approved controls and should not live on a visible label or be the only copy stored on the protected system.
Make handover a closed loop
The process starts before transport. A team should be able to account for the following sequence:
- Review the planned backup result and investigate unexpected warnings before marking the copy ready.
- Record the media identifier, backup-set reference, verification status and intended destination.
- Confirm that another known-good copy remains protected while the medium is in transit or under test.
- Hand the item to the authorised person or route, recording the release time and expected recipient.
- Obtain a receipt or confirmation of arrival, then update the register rather than assuming that dispatch equals delivery.
- On return, check the item’s status and earliest permitted reuse date before it joins the next backup cycle.
The choice of transport method depends on data sensitivity, transfer frequency, distance and the organisation’s security requirements. Regardless of the method used, every transfer should be documented to ensure that each backup medium can be tracked from dispatch through to confirmed receipt.
Example of an off-site backup tracking register
Maintaining an accurate tracking register is essential for managing off-site backup media. The example below outlines the key information to record for each medium, helping teams monitor its location, verify custody and determine when it can safely be reused.
| Field | Why it matters |
|---|---|
| Media ID | Removes ambiguity about the physical item. |
| Backup-set reference and date | Connects the medium to the intended recovery point. |
| Verification status | Shows whether the result was reviewed before release. |
| Current custodian and location | Tells the team whom to contact and where to start. |
| Released / received timestamps | Turns a handover into a traceable event. |
| Earliest reuse date | Prevents premature overwrite of a retained copy. |
| Exception and owner | Keeps a late, missing or suspect item visible. |
A short register used consistently is more valuable than a complex record that stops being updated after a few weeks. It should be readable by the person who has to act during an absence, not only by the person who created it.
Add two checklists to the routine
Before release, confirm the right medium, a reviewed backup result, a current register entry, a known destination and preservation of another usable copy. The person handing over the item should know the expected acknowledgement and what to do if it is not received.
At receipt, confirm the identifier, the agreed storage location and the arrival record. If anything differs, record it as an exception and notify the responsible person. Do not wait for the next rotation to discover that a copy has never arrived or cannot be identified.
During a recovery request, use the same register to obtain the item through the normal custody route. Record the time needed to request, locate, retrieve, prepare and restore the agreed data scope. This is the evidence that connects off-site custody to a recovery objective.
Handle late or missing media without sacrificing the last good copy
Media can be late, unavailable, damaged or unexpectedly needed for an investigation. A resilient procedure makes the next action explicit: who assesses the exception, which spare may be used, which copy must remain untouched and when the rotation can return to normal. An operational reserve is useful because it prevents the team from overwriting the last known-good copy merely to keep a calendar date.
An incident involving a medium may trigger additional internal actions depending on the data, contract and local obligations. Report it promptly through the organisation’s established route, preserve the facts in the register and do not describe the copy as available until its status has been confirmed.
Test the complete journey, not only the backup job
Periodically select a representative, non-current set and ask for it through the documented route. The exercise should include locating it in the register, collecting it from the secondary location, preparing the required equipment and restoring an agreed scope for business validation. Measure the entire path, not just the data-transfer time.
If the exercise misses the recovery expectation, identify the cause: location, access, responsibilities, documentation, hardware or backup dependencies. Update the procedure and repeat the relevant test. That work is what turns an off-site copy into a usable part of the recovery plan.
To strengthen your backup strategy, explore our guides on offline media rotation, the 3-2-1-1-0 backup rule and restore testing best practices.
Tandberg Data RDX solutions provide removable storage options for off-site backup strategies. Explore our RDX drives and cartridges to find a solution suited to your storage capacity, media rotation and recovery requirements.
Share this guide